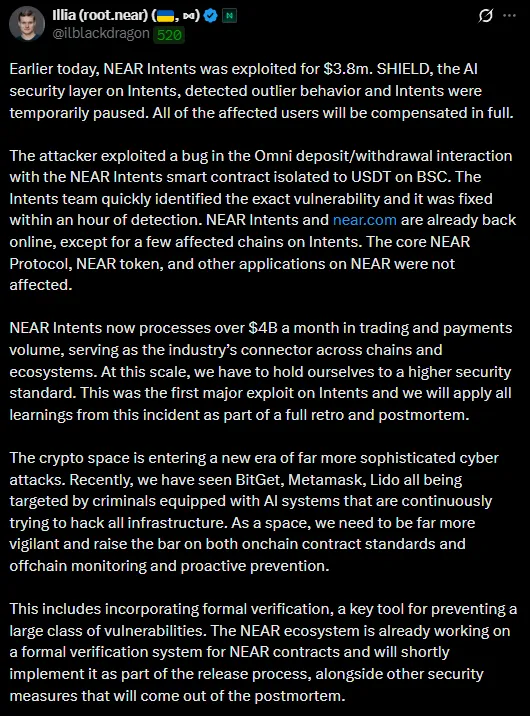
- The bug was isolated in the Omni infrastructure chain with USDT on BSC during deposits/withdrawals via the NEAR Intents smart contract
- The anomaly was detected by SHIELD—the project’s proprietary AI monitoring layer—after which the service was temporarily suspended
- The vulnerability was patched within an hour of discovery; NEAR Intents is now back online, except for a few isolated networks
- The core NEAR protocol and token were not affected—this is the first major exploit targeting Intents, which currently processes over $4 billion in monthly volume
Polosukhin noted the rise in attacks leveraging AI systems against large-scale infrastructure, citing recent incidents involving Bitget, MetaMask, and Lido.
NEAR plans to introduce formal contract verification into its release process and has invited other projects to join SHIELD for threat data sharing. A full analysis of the incident will be published in the coming days.